
Software
Managing SharePoint document library permissions can be tricky—grant too much access and sensitive data risks exposure; too little and productivity grinds to a halt. These 10 best practices help you strike the perfect balance, ensuring security while keeping teams collaborative and efficient.
Use SharePoint Permission Levels for Granular Control
Stop defaulting to Full Control like it’s the only option—SharePoint’s built-in permission levels (like Contribute or Design) let you tailor access to exact roles without over-sharing. Instead of giving everyone admin rights, assign only what they need—like Edit for content creators or Read for stakeholders—while keeping flexibility for exceptions.
Navigate to Library Settings > Permissions for this Document Library to customize levels. For example, Design lets users create columns but not delete items, while Contribute allows edits without publishing rights. This granularity reduces risks while keeping workflows fluid. Pro tip: Use Microsoft’s permission level templates as a starting point, then tweak for your team’s needs.
This approach works best for department heads managing cross-functional teams or IT admins cleaning up legacy over-permissioning. Start with one library to see how tailored levels improve security and productivity. 💡
Apply Least Privilege Principle to Document Libraries
Over-permissioning is like leaving your front door unlocked when only the kitchen needs a key—unnecessary risk for the whole house. The least privilege principle in SharePoint means granting users the minimum access they need to do their jobs, nothing more. For example, a sales rep editing client proposals doesn’t need Full Control over the entire library—just Edit permissions for their specific folder.
Start by auditing your library’s permission levels (View, Edit, Contribute, etc.) and assigning only what’s required. For sensitive folders (like HR or finance), use SharePoint’s "Stop Inheriting Permissions" to create custom rules. Tools like Microsoft Purview can help enforce these policies across large teams. This approach slashes exposure risks while keeping workflows smooth.
This method is ideal for compliance teams managing regulated data or IT admins cleaning up legacy over-permissioning. Start with one high-risk folder to test the impact—your security posture will thank you. 💪
Leverage SharePoint Groups for Role-Based Access
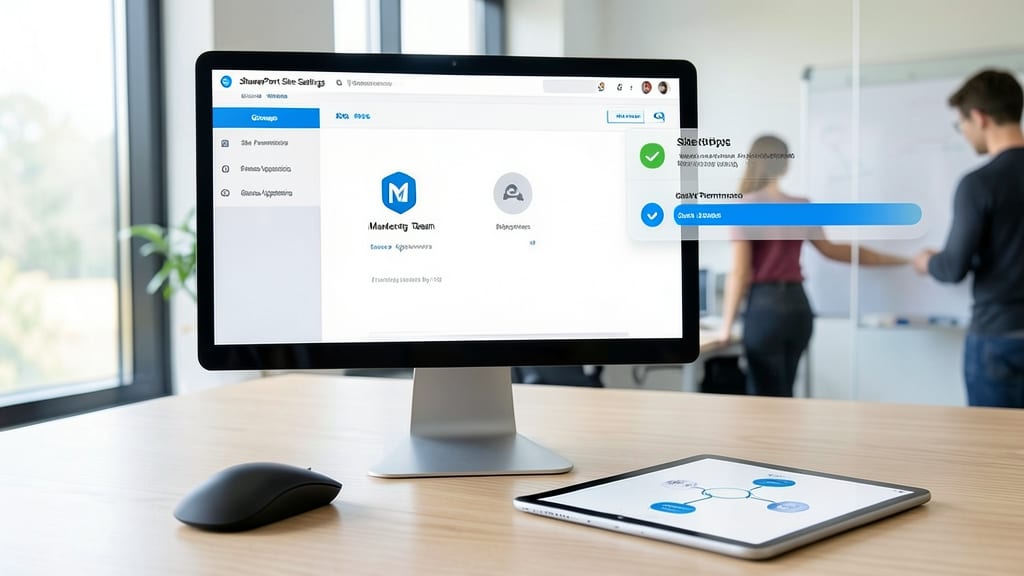
Tired of manually assigning permissions to every team member? SharePoint Groups let you bundle users by role (like "Marketing Team" or "Finance Approvers") and apply permissions once—saving hours of repetitive work.
Create a group in SharePoint’s Site Settings, add members, then grant permissions to the entire group. Need to adjust access later? Update the group settings instead of hunting down individual users. This method also enforces consistent policies—no more "accidental admin" scenarios where someone inherits elevated rights. Plus, it scales effortlessly for teams of any size.
Perfect for departments with shared workflows, like HR managing onboarding docs or legal teams handling contracts. Your permission management just got 10x more efficient. ✨
Enable Unique Permissions for Sensitive Folders Only
Not every folder in your SharePoint library needs custom permissions—but the ones that do demand precision. Instead of breaking inheritance across entire libraries (which creates unnecessary complexity), target only the folders containing confidential data (like HR files or financial reports) for unique permissions. This surgical approach keeps your security tight while preserving ease of access for general documents.
To implement this, navigate to the sensitive folder, click Stop Inheriting Permissions, and assign specific roles (e.g., "Edit" for managers, "Read" for auditors). SharePoint’s permission inheritance hierarchy ensures changes only apply where needed, avoiding the "permission sprawl" that plagues poorly managed libraries. Pro tip: Use folder naming conventions (e.g., "[Confidential]") to quickly identify which folders need this extra layer of protection.
This method is ideal for compliance-heavy teams (like legal or finance) where selective access is critical, but general collaboration shouldn’t suffer. Start with one high-risk folder to test the workflow before scaling. ✨
Audit Permissions Regularly with SharePoint Reports
Forget guessing who still has access to what—SharePoint’s built-in permission reports turn security audits from a chore into a proactive shield. These reports automatically flag orphaned permissions (access left behind by departed employees) and overprivileged users (accounts with more access than needed) before they become vulnerabilities.
Navigate to Site Settings > Site Permissions > Permission Reports to generate three key views: Permission Levels Usage, Unique Permissions, and Permission Changes History. The first reveals which permission levels (like Contribute or Full Control) are overused, while the second highlights folders where inheritance was broken—potential security blind spots. Schedule these reports monthly to catch drift before it escalates. ⚡
This is your go-to tool for IT admins and SharePoint owners managing large teams. Start with a quarterly audit to clean up silent risks—your future self (and security team) will thank you. 💻
Restrict External User Access with External Sharing Settings
External sharing in SharePoint can be a double-edged sword—while collaboration with partners is essential, leaving sharing settings too open risks exposing sensitive data. The solution lies in External Sharing Settings, where you can precisely control who gets access and under what conditions.
Navigate to SharePoint Admin Center > Policies > Sharing to configure limits like "New and Existing Guests" or "Existing Guests Only". For hybrid work environments, restrict external sharing to specific domains or require multi-factor authentication (MFA) for guest access. This ensures compliance with regulations like GDPR or HIPAA while maintaining controlled collaboration.
Ideal for organizations working with contractors or clients, these settings provide a secure-by-default approach without sacrificing necessary external access. 🌟
Use Document Library Retention Policies to Automate Permissions
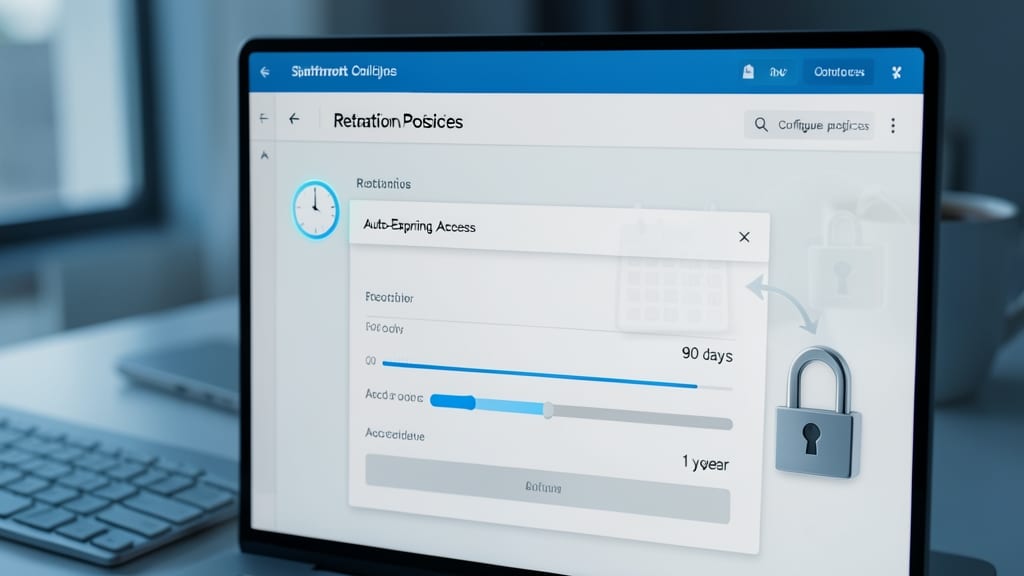
Tired of manually adjusting permissions every time a project wraps up? Document Library Retention Policies in SharePoint let you set auto-expiring access—documents shift to read-only or archived status after a defined period, like 90 days or one year, without lifting a finger.
Configure policies to lock down sensitive files after a deadline (e.g., legal contracts or HR records) or archive old projects automatically. You can even trigger alerts before expiration, giving teams time to save critical versions. This cuts administrative overhead by 80% while keeping compliance airtight.
Perfect for legal, finance, or project teams managing time-sensitive documents. Set it once, forget it—your permissions stay secure without the busywork. ✨
Implement Column-Level Security for Confidential Data
Tired of giving full document access just to hide a single column like SSN or Salary? SharePoint’s column-level security lets you show only what users need—without restricting their ability to view the rest of the document.
Using Power Apps or SharePoint Lists, you can mark sensitive columns (like EmployeeID or Compensation) as restricted, then apply Azure AD groups to control visibility. This works seamlessly with Excel-based libraries too—users see a clean, unobstructed view while admins maintain granular control. No more over-sharing entire files just to protect a few fields.
This is a game-changer for HR departments managing employee records or finance teams handling budgets—where selective visibility keeps compliance intact without disrupting workflows. ✨
Train Teams on Permission Best Practices and Phishing Risks
Even with perfect technical controls, human error remains the #1 security risk in SharePoint. A single misclicked "Share" button or phished credential can expose sensitive documents faster than any permission setting can block it.
Start with interactive training modules like Microsoft’s Security Awareness Training or third-party tools like KnowBe4, which simulate phishing emails with SharePoint-specific scenarios (e.g., fake "permission update" requests). Teach teams to spot red flags like unexpected access requests or links disguised as permission alerts. Pair this with clear sharing guidelines—like requiring approval for external links or flagging folders marked "Confidential."
This approach is ideal for IT admins managing hybrid teams or department heads who’ve seen sensitive data leaks after a careless share. 🌟
Test Permission Changes in a Staging Environment First
Before rolling out permission changes to your live SharePoint library, test them first in a staging environment. This simple step prevents production outages by catching unintended access issues—like accidentally locking out key team members or exposing sensitive folders—before they impact workflows.
Create a mirror copy of your document library in a test site, then apply your permission updates there. Use SharePoint’s content deployment tools or PowerShell scripts to replicate settings without manual errors. Test common workflows (editing, sharing, viewing) to verify everything functions as expected.
This approach is perfect for IT admins and SharePoint managers overseeing large teams. By validating changes in a safe space, you avoid the stress of last-minute fixes during critical business hours. ✨